Our research found 49 publicly disclosed data breaches and cyber attacks in October 2026, with at least 67,588,661 records confirmed as breached. That total is a floor: it counts only figures confirmed by the organisation affected, a regulator or an independent researcher. It leaves out about 19 million records that attackers or the media have claimed and about 46 million that organisations say only may have been exposed. Last month’s report counted 40 incidents and at least 252.8 million records.
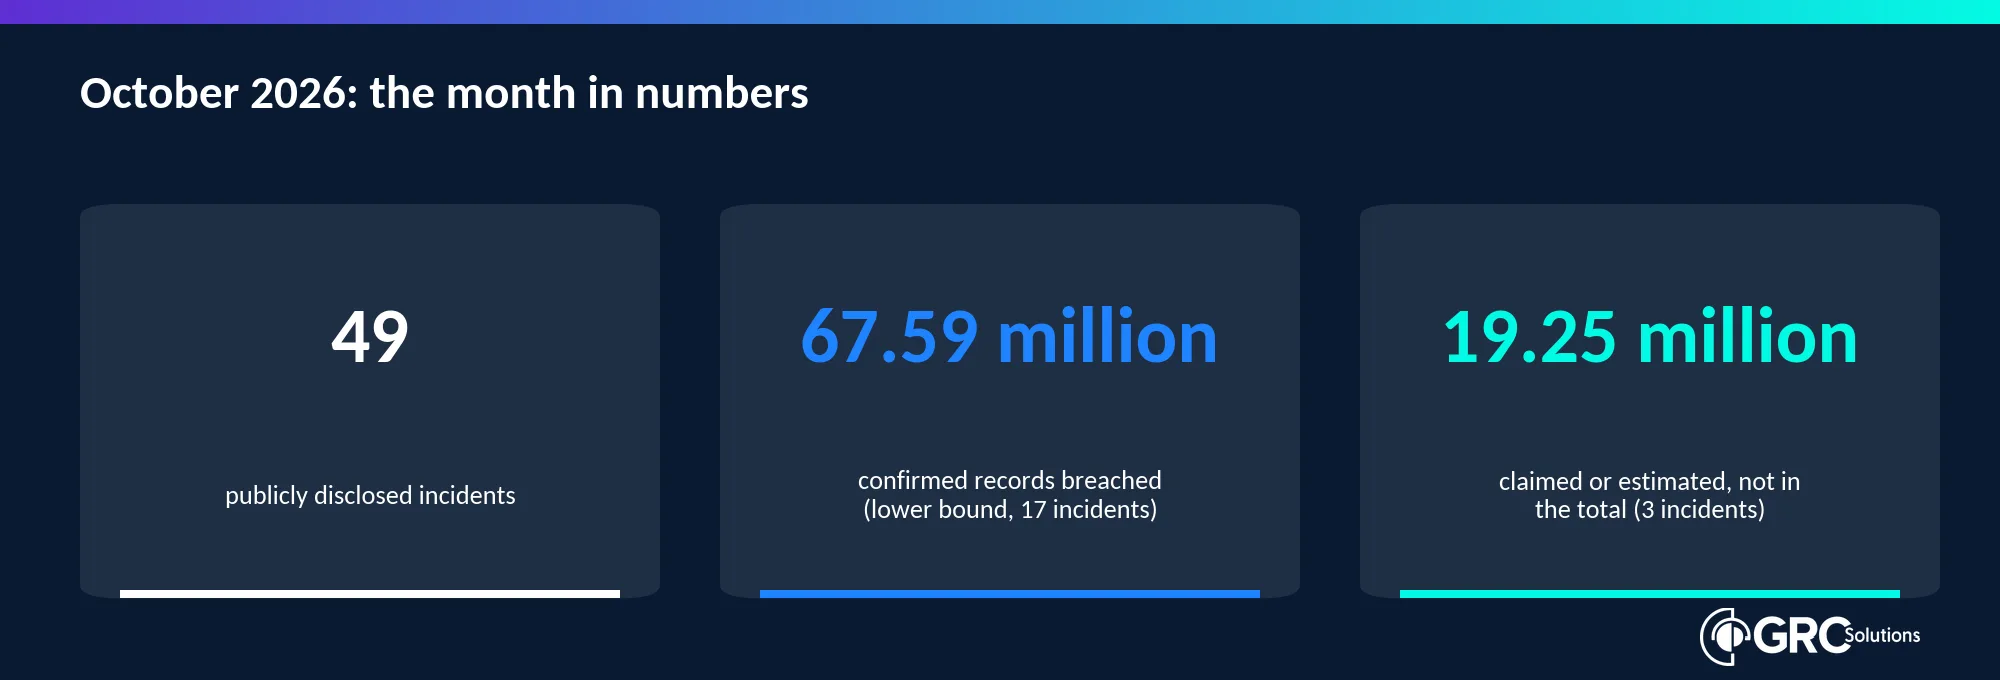
The month in numbers: 49 incidents, 67.6 million confirmed records and 19.25 million claimed or estimated records that are not in the total.
Summary
- Total number of incidents disclosed: 49
- Total number of confirmed records breached (lower bound): 67,588,661, from 17 incidents
The number of breached records comprises those verified by the affected organisation, a regulator or independent researcher analysis.
It excludes 3 incidents that rest on attacker claims or media estimates, 8 incidents where the organisation gives only a maximum or says data may have been exposed, and 21 incidents with no figure at all, such as cryptocurrency thefts and attacks where the organisation has not said how many people were affected.
The units differ (accounts, individuals, records, email addresses) and are summed as reported. Several organisations count records rather than people, so the true number of affected individuals is lower.
Two large figures that are not in the total
Two figures are large enough that, if verified, both would rank among the month’s five largest incidents. Neither is confirmed, so we have left them out of the confirmed total and the top five below and summarise them here instead.
Sourcenext
- Records affected: Up to 22,519,960 records. The company says these are the records that may have been leaked, not a confirmed number of affected individuals.
- Data: Names, email addresses, phone numbers, addresses, workplaces, job titles and passwords. Credit card information was not included.
- Cause: A third party misused the API that retrieves member information from 9 October, and Sourcenext found and contained the access on 13 October.
- Status: Announced by the company on 15 October. Sourcenext reset every password and is emailing affected customers.
Pathao
- Records affected: About 19.06 million accounts (claimed). The attackers say they hold 250 million records across 591 databases. Pathao has not given a count.
- Data: Pathao confirms that names, email addresses and phone numbers were taken. The attackers also claim national ID numbers, driving licence details, photographs and home addresses.
- Cause: Not disclosed. Pathao detected the incident on 4 October and shut down some critical systems as a precaution.
- Status: Unauthorised access confirmed by the company on 7 October. The scale and the attackers’ US$400,000 ransom demand are unverified.
Top five incidents by number of confirmed records affected
The five largest incidents publicly disclosed in October 2026, ranked by confirmed number of records (attacker claims and unconfirmed maximums are covered separately above):
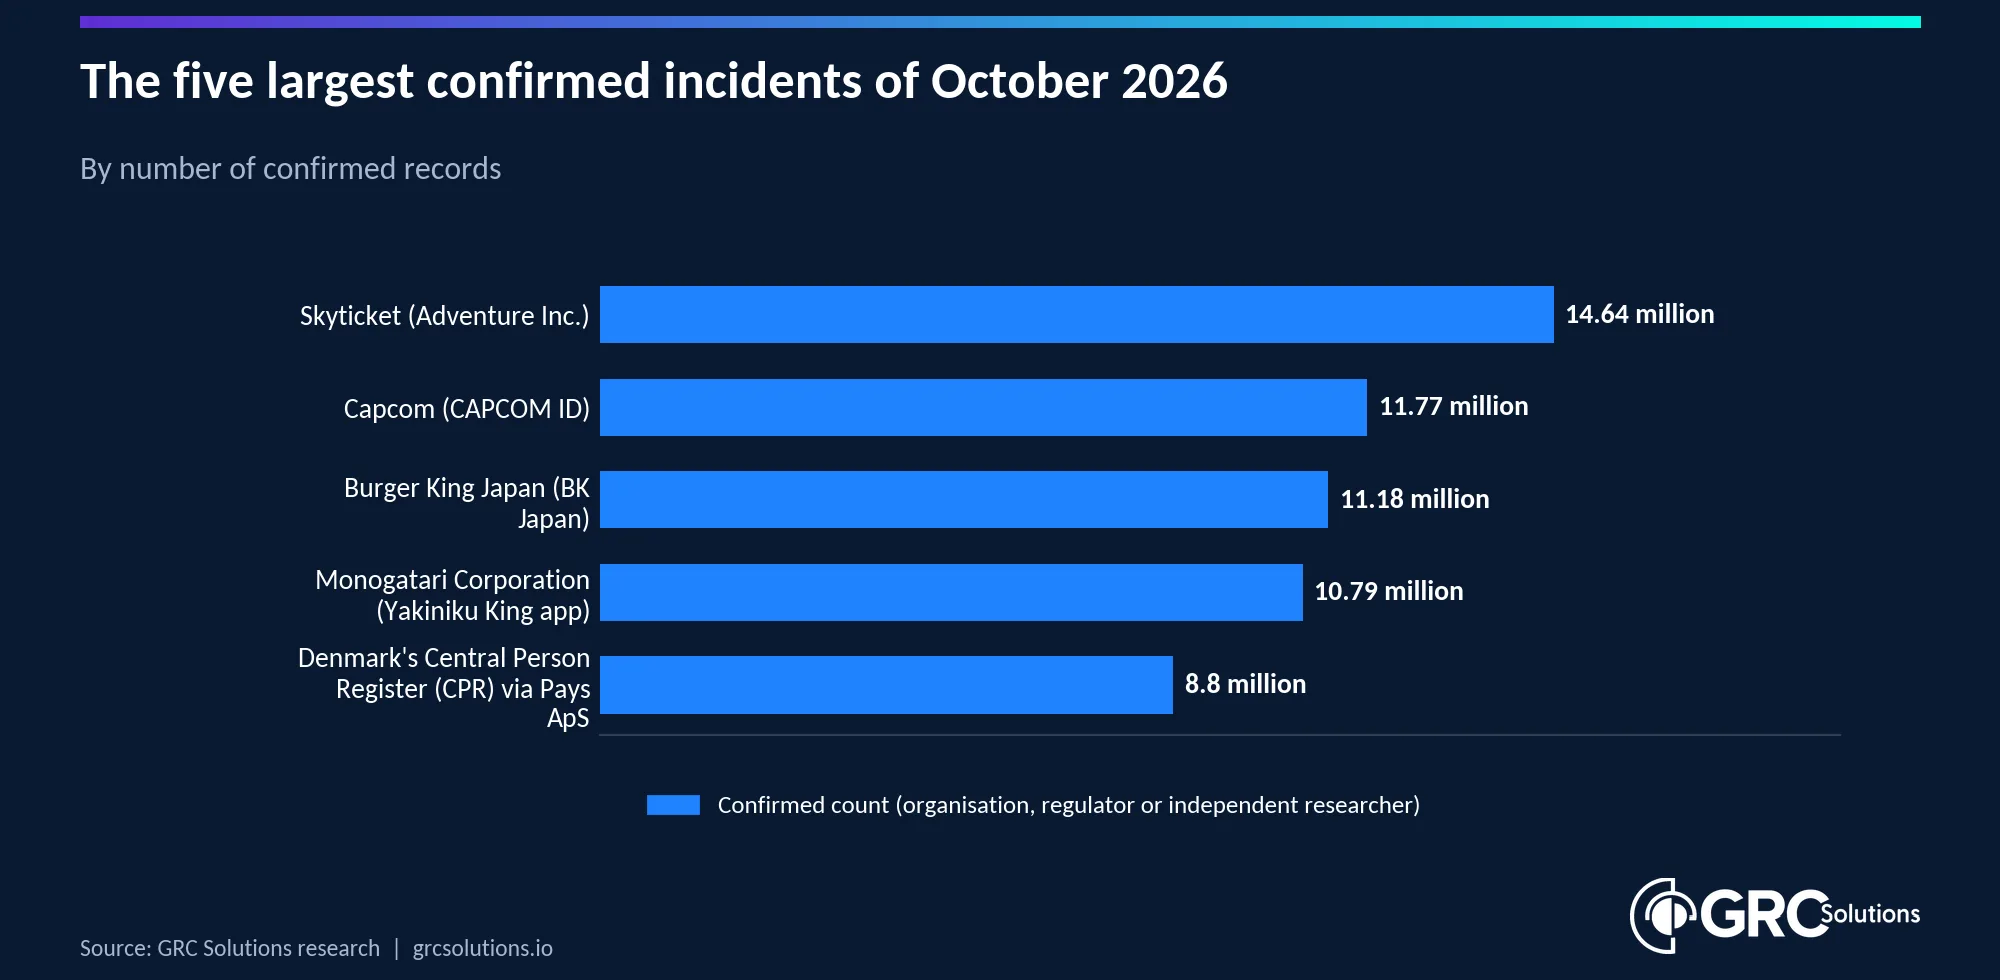
The five largest incidents by number of confirmed records, ranked from the largest.
1. Skyticket (Adventure Inc.)
- Records affected: About 14.64 million items of customer information (confirmed by the company). The items include duplicates, so they are not unique people.
- Data: Names (including passport spelling), dates of birth, email addresses, phone numbers and addresses; hashed passwords for about 4.13 million; bank account details in some cases. Passport numbers were not leaked.
- Cause: Three separate unauthorised accesses by different routes, the largest on 2 to 4 October. The company has not said how the attackers got in.
- Status: Confirmed by Adventure Inc. on 9 October. It has confirmed one case of misuse and suspended saved-card payments.
2. Capcom (CAPCOM ID)
- Records affected: 11,774,247 records (confirmed by the company).
- Data: Email addresses, login IDs, account creation and last-access dates, login counts and recent IP addresses. No passwords or payment card details were taken.
- Cause: An external party gained unauthorised access on 19 October to databases holding CAPCOM ID records. The company has not said how.
- Status: Confirmed by Capcom on 22 October. The attacker changed the passwords on 196 accounts, and games are unaffected.
3. Burger King Japan
- Records affected: About 11.18 million member records (confirmed by the company). The company counts records, not unique people.
- Data: Member ID, email address, name, phone number, date of birth, gender, prefecture of residence and registration type. No card details were taken, and a password leak is not confirmed.
- Cause: Unauthorised third-party access, from 2 to 7 October, to the backend that manages member information for the official app. The company has not said how.
- Status: Confirmed on 15 October and reported to Japan’s Personal Information Protection Commission. No secondary harm has been found.
4. Monogatari Corporation (Yakiniku King)
- Records affected: 10,788,963 member records, out of 10,808,784 registered users (confirmed by the company).
- Data: Email addresses, phone numbers and other member details.
- Cause: Unauthorised access, detected on 2 October, to the member management system of the Yakiniku King reservation and rewards app. The company has not said how.
- Status: Announced on 5 October. No misuse has been confirmed.
5. Denmark’s Central Person Register (CPR)
- Records affected: About 8.8 million registered persons, living, emigrated and dead (confirmed by the government).
- Data: Names, addresses and CPR (national identity) numbers.
- Cause: Someone misused the lawful search access of a two-person IT supplier, Pays ApS. A person claiming the breach told Politiken that at least three Pays accounts, including the administrator account, used the password ‘123456’; the government has not confirmed that.
- Status: Announced on 5 October. Authorities blocked the supplier’s access and police are investigating.
Trends in October 2026
Last month’s report counted 40 incidents, so we can compare this month with it. Differences in the confirmed total mostly reflect individual large incidents.
- Japan accounted for 17 of the 49 incidents. It had 7 of September’s 40. Four of the five largest incidents this month were Japanese (Skyticket, Capcom, Burger King Japan and Monogatari), and Japan’s confirmed counts add up to 55.8 million records. Japan’s prime minister called a cabinet meeting on 26 October to discuss the attacks.
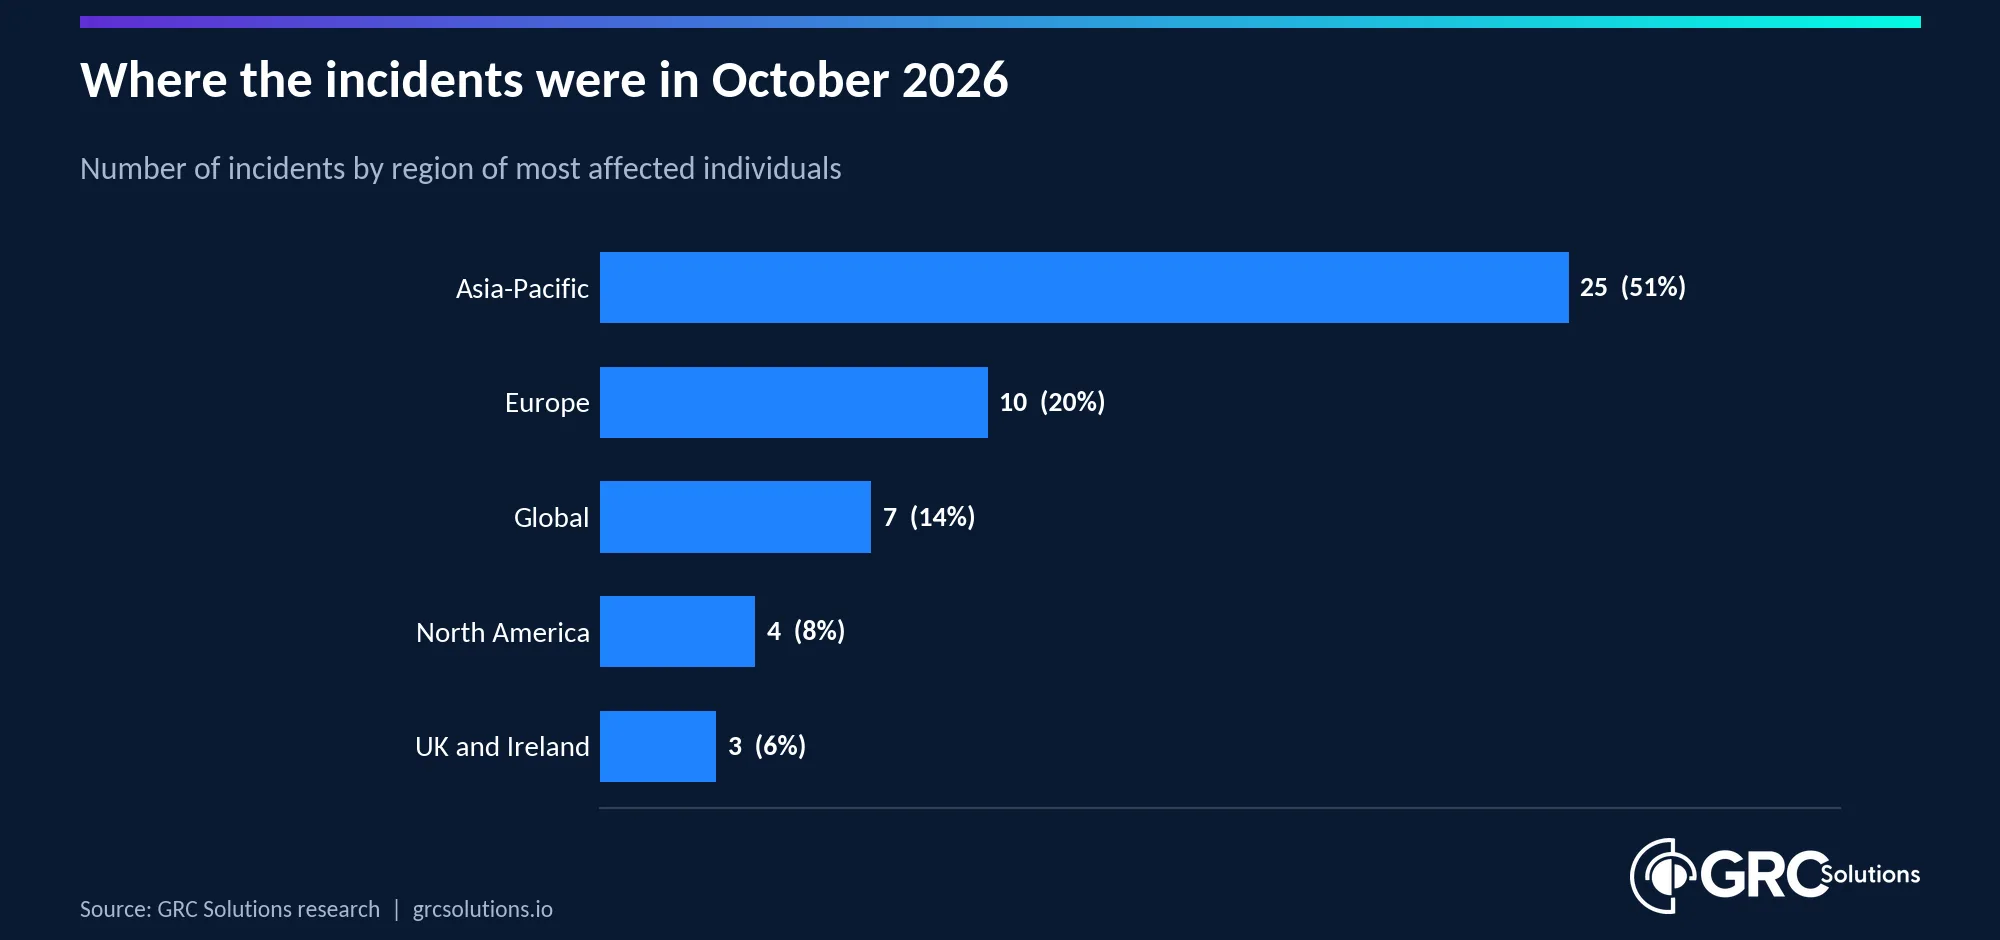
Incidents by region of most affected individuals: Asia-Pacific 25, Europe 10, Global 7, North America 4, UK and Ireland 3.
- Suppliers and shared platforms were the route in for 23 incidents. The Amadeus reservation system accounts for 7 (the supplier and 6 airlines), the IDC Frontier ransomware attack on a Cloud provider for 3 (the provider, JR East and JR Kyushu) and attacks on refrigeration equipment suppliers for 5 French supermarket chains. Other incidents ran through suppliers to Denmark’s population register, a Swiss pension fund, a karaoke chain and an Australian cosmetics brand. We list each victim separately in the table below.
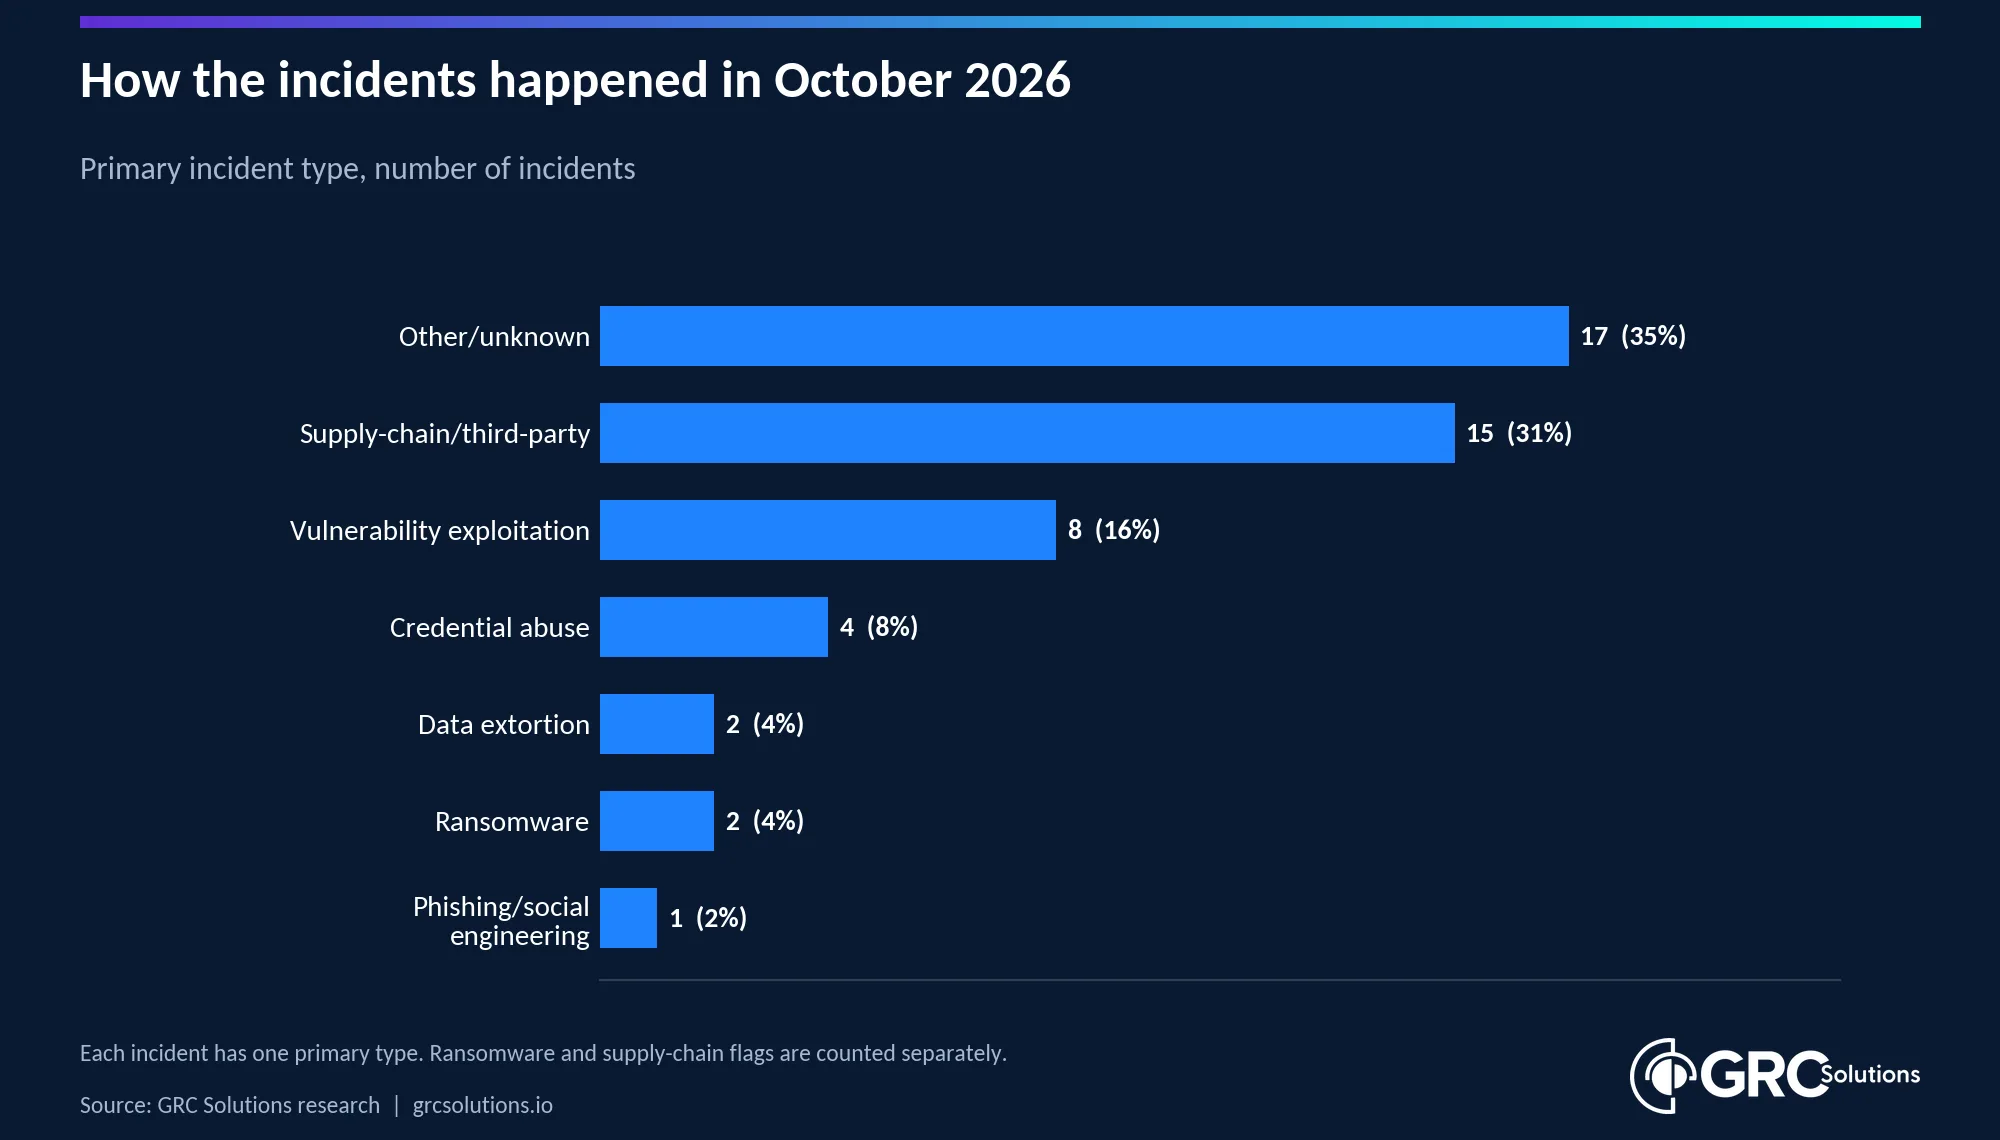
Incidents by primary type. Each incident has one primary type; ransomware and supply-chain involvement are flagged separately.
- 8 organisations gave only a maximum or a possible figure. Together those figures come to about 46 million records, against 67.6 million confirmed. Sourcenext, Daiichi Kosho, Bookoff, JR East and JR Kyushu all said their records may have been exposed rather than confirming theft.
- Cryptocurrency thefts have no record counts. Binance estimates the impact of its theft at about US$6.3 billion, with about US$3 billion frozen, and TRM Labs and Chainalysis attribute it to the North Korean group TraderTraitor with a high degree of confidence. Polymarket lost about US$2.5 million to US$2.7 million through a compromised third-party script. We list both in the table but do not rank them.
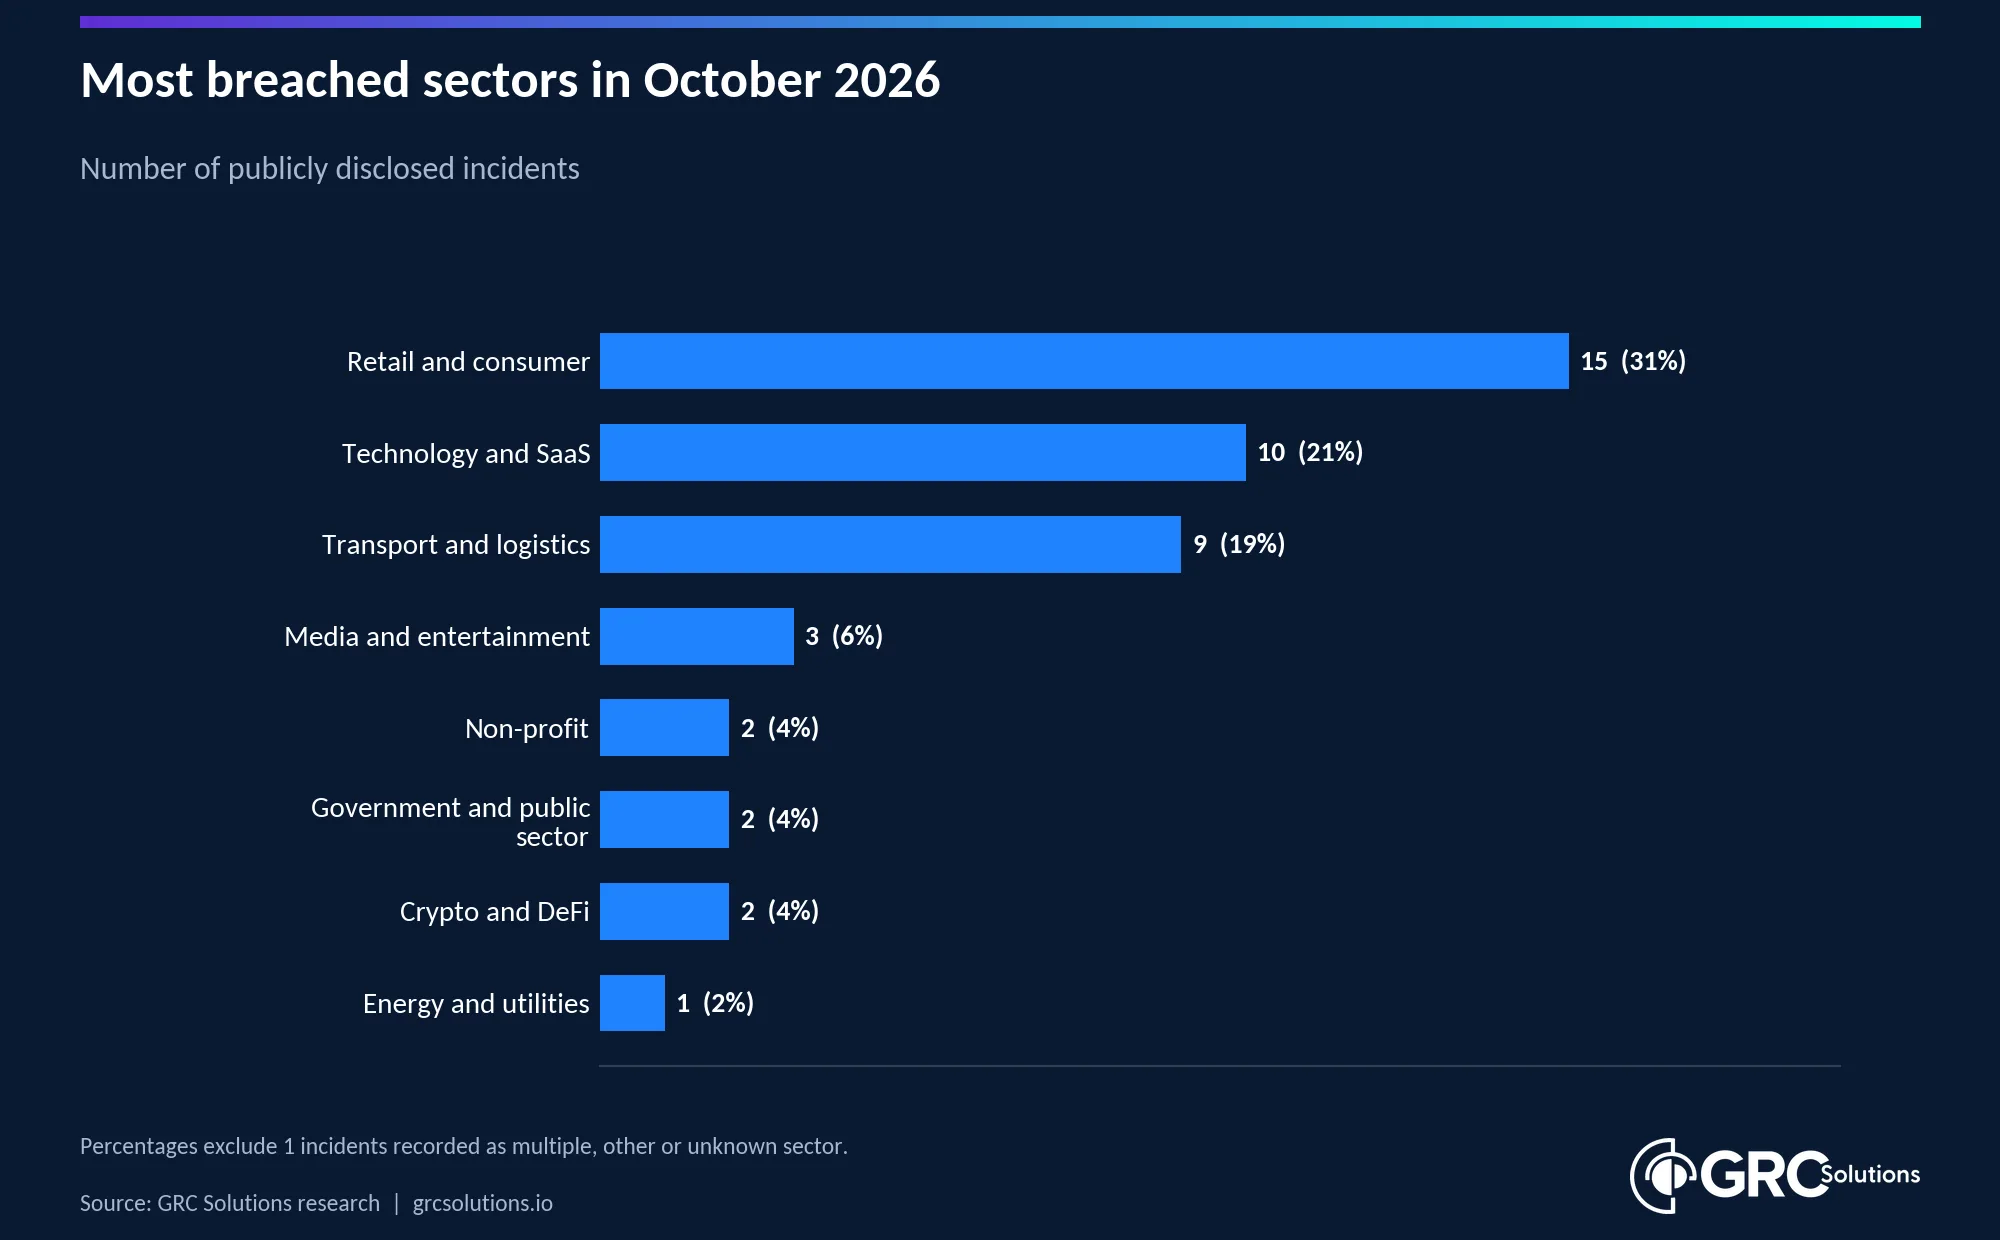
Most breached sectors by number of incidents: retail and consumer leads with 10.
Key vulnerabilities exploited
- Stolen, weak or unrevoked credentials: the person who breached Denmark’s population register says three supplier accounts used the password ‘123456’; attackers used valid login credentials for an Amadeus system account for about three years; stolen credentials opened Nikkei’s cloud service; Zeabur’s plain-text admin credentials survived a password rotation; and Railway’s attacker used CI credentials to decrypt customers’ stored secrets.
- Unpatched or exposed software: attackers exploited a critical vulnerability in VMmanager 6 at the Russian hosting provider FirstVDS, a legacy analytics tool at Double Counter and an unspecified flaw at Ricardo. In France, attackers took over refrigeration controllers made by Danfoss, Copeland and Dixell at about 700 supermarkets.
- Misused interfaces and trusted components: Sourcenext’s member API returned customer data to a third party, a compromised DebugBear monitoring script drained Polymarket users’ wallets, and a malicious LiteLLM release built from a lookalike repository reached PyPI and Docker Hub.
- Social engineering and compromised devices: ASOS says an attacker impersonated a trusted contact to get an employee’s login and Binance’s preliminary finding is that a compromised DevOps engineer’s laptop led to a service container that submitted unauthorised withdrawals.
List of data breaches and cyber attacks disclosed in October 2026
| Disclosure date | Organisation | Country | Sector | Incident type | Records affected | Status |
| 05-10-2026 | Denmark’s Central Person Register (CPR) via Pays ApS | Denmark | Government and public sector | Supply-chain/third-party | About 8.8 million people | Confirmed |
| 05-10-2026 | Monogatari Corporation (Yakiniku King app) | Japan | Retail and consumer | Other/unknown | 10,788,963 records | Confirmed |
| 05-10-2026 | Southern Company (Georgia Power, Alabama Power, Mississippi Power) | USA | Energy and utilities | Other/unknown | About 400,000 accounts | Confirmed |
| 06-10-2026 | ASOS | UK | Retail and consumer | Phishing/social engineering | Not disclosed | Confirmed |
| 06-10-2026 | Double Counter (Tellter SAS) | France | Technology and SaaS | Vulnerability exploitation | About 1 million email addresses | Confirmed |
| 06-10-2026 | Jefferson County, Missouri | USA | Government and public sector | Other/unknown | Not disclosed | No evidence of data theft |
| 06-10-2026 | Nikkei Inc. | Japan | Media and entertainment | Credential abuse | About 1.83 million records | Confirmed |
| 06-10-2026 | University of Illinois Chicago College of Medicine | USA | Education | Ransomware | Not disclosed | Unconfirmed |
| 07-10-2026 | IDC Frontier (IDCF Cloud, a SoftBank subsidiary) | Japan | Technology and SaaS | Ransomware (supply chain) (ransomware) | n/a (495 client organisations disrupted) | No evidence of data theft |
| 07-10-2026 | Pathao | Bangladesh | Transport and logistics | Data extortion | 19.06 million accounts (claimed) | Confirmed |
| 07-10-2026 | SaRang Church | South Korea | Non-profit | Other/unknown | About 89,000 members (reported) | Unconfirmed |
| 07-10-2026 | Yoido Full Gospel Church | South Korea | Non-profit | Other/unknown | About 850,000 members (potential) | Confirmed |
| 08-10-2026 | Daiichi Kosho (via contractor Nippon Columbia Group) | Japan | Media and entertainment | Supply-chain/third-party | About 8.72 million records (potential) | Unconfirmed |
| 08-10-2026 | Lawson | Japan | Retail and consumer | Other/unknown | 2,155,345 records | Confirmed |
| 08-10-2026 | Publica (federal pension fund) via PK Softech | Switzerland | Finance and insurance | Supply-chain/third-party | More than 100,000 insured people (estimate) | Confirmed |
| 09-10-2026 | Bookoff Group Holdings | Japan | Retail and consumer | Other/unknown | Up to 6.43 million accounts | Confirmed |
| 09-10-2026 | East Japan Railway Company (JR East) and View Card | Japan | Transport and logistics | Supply-chain/third-party (ransomware) | About 6.09 million accounts (potential) | Unconfirmed |
| 09-10-2026 | JR Kyushu | Japan | Transport and logistics | Supply-chain/third-party (ransomware) | Up to 1.3 million email addresses (potential) | Unconfirmed |
| 09-10-2026 | Ricardo (SMG Swiss Marketplace Group) | Switzerland | Retail and consumer | Vulnerability exploitation | About 890,000 accounts | Confirmed |
| 09-10-2026 | Skyticket (Adventure Inc.) | Japan | Retail and consumer | Other/unknown | About 14.64 million records | Confirmed |
| 09-10-2026 | Webbers Estate Agents | UK | Other | Supply-chain/third-party | Not disclosed | Unconfirmed |
| 11-10-2026 | Carrefour (refrigeration controllers) | France | Retail and consumer | Vulnerability exploitation (supply chain) | n/a (about 80 supermarkets) | Confirmed |
| 11-10-2026 | Coopérative U (refrigeration controllers) | France | Retail and consumer | Vulnerability exploitation (supply chain) | n/a (nearly 100 stores; its chief executive called the attack ‘unprecedented’) | Confirmed |
| 11-10-2026 | E.Leclerc (refrigeration controllers) | France | Retail and consumer | Vulnerability exploitation (supply chain) | n/a (several stores; E.Leclerc confirmed to AFP that a refrigeration equipment supplier was attacked) | Confirmed |
| 11-10-2026 | Intermarché (refrigeration controllers) | France | Retail and consumer | Vulnerability exploitation (supply chain) | n/a (150 to 200 stores) | Confirmed |
| 11-10-2026 | Monoprix (refrigeration controllers) | France | Retail and consumer | Vulnerability exploitation (supply chain) | n/a (about 5% of its roughly 490 French stores) | Confirmed |
| 12-10-2026 | Ahold Delhaize | Netherlands | Retail and consumer | Other/unknown | Not disclosed | No evidence of data theft |
| 15-10-2026 | Burger King Japan (BK Japan) | Japan | Retail and consumer | Other/unknown | About 11.18 million records | Confirmed |
| 15-10-2026 | Sourcenext | Japan | Technology and SaaS | Other/unknown | 22,519,960 records (potential) | Confirmed |
| 16-10-2026 | Fancl and Attenir (Kirin Holdings group) | Japan | Retail and consumer | Other/unknown | 785,496 people (834,947 records) | Confirmed |
| 17-10-2026 | Napoleon Perdis (via Retail Express) | Australia | Retail and consumer | Supply-chain/third-party | Almost 340,000 customers | Confirmed |
| 17-10-2026 | Zeabur | Not stated | Technology and SaaS | Credential abuse | 321,810 accounts | Confirmed |
| 19-10-2026 | FirstVDS | Russia | Technology and SaaS | Vulnerability exploitation | Not disclosed | Confirmed |
| 21-10-2026 | GMO Internet (Onamae.com Desktop Cloud) | Japan | Technology and SaaS | Data extortion (supply chain) | Up to 26,739 servers (potential) | Confirmed |
| 21-10-2026 | LiteLLM | Not stated | Technology and SaaS | Supply-chain/third-party | n/a (malicious release for under 3 hours) | Confirmed |
| 21-10-2026 | Railway | Not stated | Technology and SaaS | Credential abuse | Up to 100,000 workspaces | Confirmed |
| 22-10-2026 | Capcom (CAPCOM ID) | Japan | Media and entertainment | Other/unknown | 11,774,247 records | Confirmed |
| 22-10-2026 | Quest Diagnostics | USA | Healthcare | Other/unknown | Not disclosed | Confirmed |
| 23-10-2026 | Amadeus IT Group (passenger service system) | Spain | Technology and SaaS | Credential abuse (supply chain) | n/a (supplier; airlines listed separately) | Confirmed |
| 23-10-2026 | Asiana Airlines (via Amadeus) | South Korea | Transport and logistics | Supply-chain/third-party | Not disclosed | Confirmed |
| 23-10-2026 | Korean Air (via Amadeus) | South Korea | Transport and logistics | Supply-chain/third-party | Not disclosed | Confirmed |
| 27-10-2026 | Sony Network Communications (So-net and plala) | Japan | Telecoms | Other/unknown | More than 2.5 million people | Confirmed |
| 28-10-2026 | 123 Reg | UK | Technology and SaaS | Other/unknown | Not disclosed | Confirmed |
| 28-10-2026 | Japan Airlines and Japan Transocean Air (via Amadeus) | Japan | Transport and logistics | Supply-chain/third-party | 92,000 customers | Confirmed |
| 29-10-2026 | All Nippon Airways (ANA) (via Amadeus) | Japan | Transport and logistics | Supply-chain/third-party | About 37,800 customers | Confirmed |
| 29-10-2026 | Binance | Not stated | Crypto and DeFi | Other/unknown | n/a (about US$6.3bn estimated impact) | Confirmed |
| 29-10-2026 | Polymarket (via DebugBear script) | Not stated | Crypto and DeFi | Supply-chain/third-party | n/a (about US$2.5m to US$2.7m drained) | Confirmed |
| 30-10-2026 | Cathay Pacific (via Amadeus) | Hong Kong | Transport and logistics | Supply-chain/third-party | About 53,000 bookings | Confirmed |
| 31-10-2026 | Malaysia Airlines (via Amadeus) | Malaysia | Transport and logistics | Supply-chain/third-party | Not disclosed (may have been affected) | Unconfirmed |
How we count
We record each incident under the date it first became public, whether that was a company statement, a regulator filing, a credible media report or, once a reputable outlet or regulator reports it, an attacker’s claim.
The confirmed total is a lower bound: it adds only counts verified by the organisation affected, a regulator or independent researcher analysis, and leaves out figures described as a maximum or as records that may have been exposed. The top five ranks incidents by confirmed record counts only; attacker claims and unconfirmed maximums are summarised separately. Incidents we could not verify against two independent sources are left out until we can. The units differ between incidents (accounts, individuals, records) and are summed as reported.